Engineering partnership · Cybersecurity

Observability-first cybersecurity

See every log, asset and threat in one place, and act on what matters first.

Fewer blind spots, faster triage and a clear list of risks to fix first.

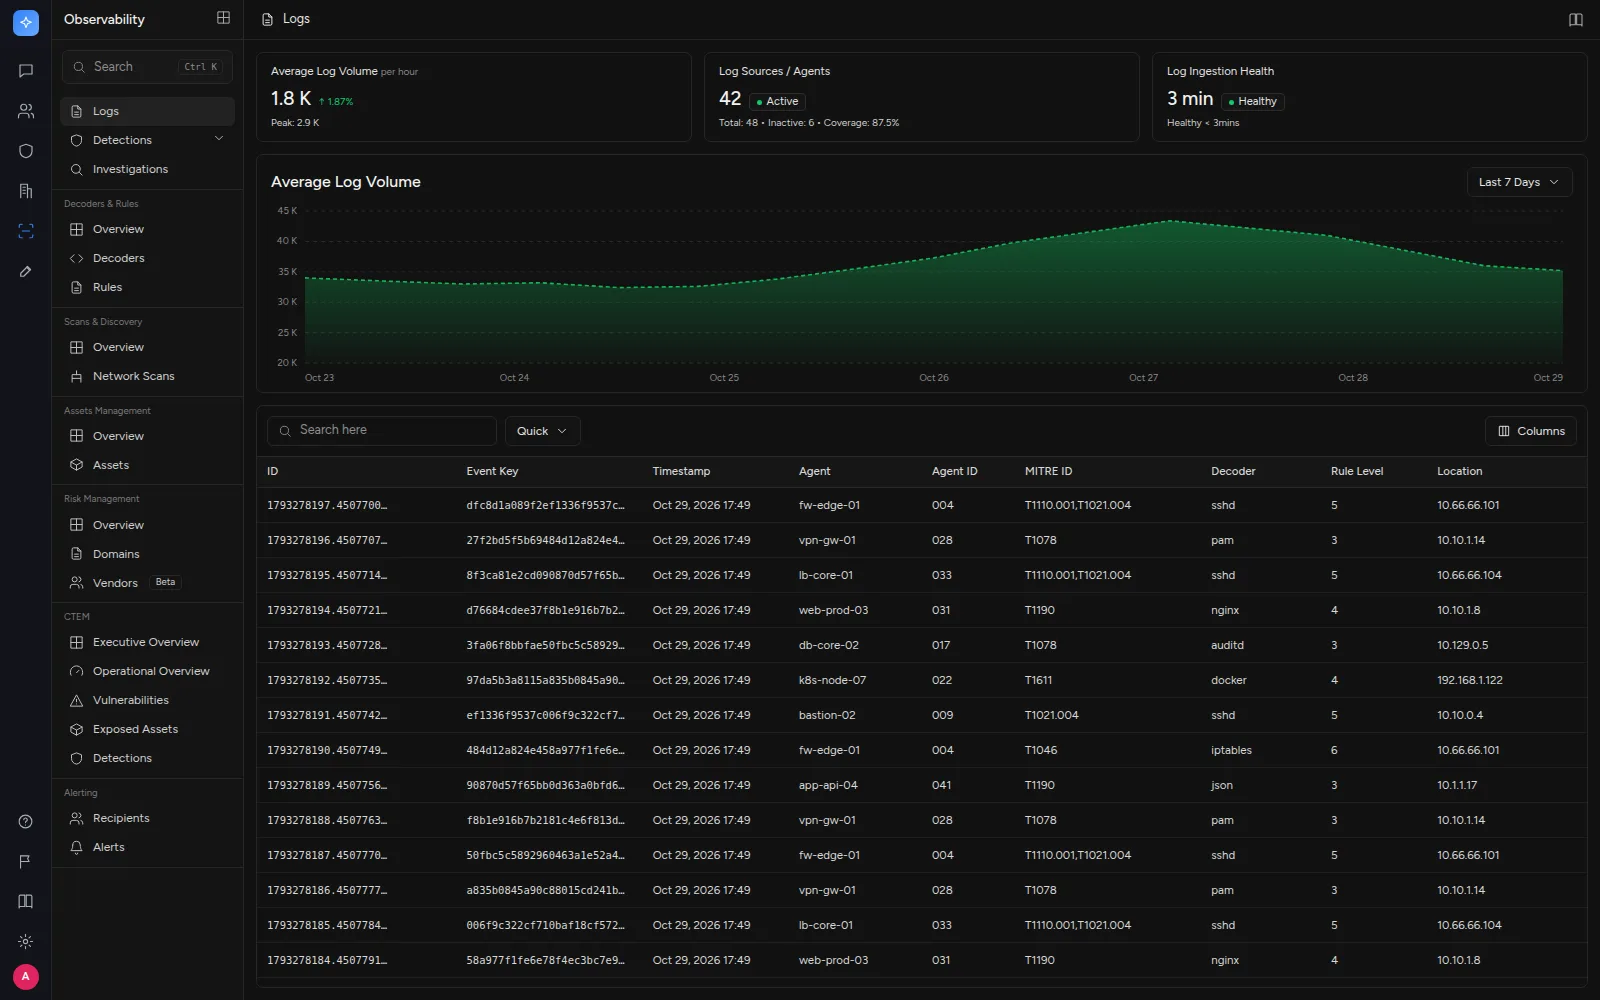
Security observability dashboard showing log volume over seven days, source health and a live table of ingested log events.
Cybersecurity

See it in action

An AI-powered security platform built on observability. It ingests your telemetry, keeps a live inventory of every asset, matches activity against an in-house threat intelligence cache and turns exposures into tracked, remediated risks.

  • 0modules
  • 0public intel feeds
  • 0bill-of-materials views
Security observability dashboard showing log volume over seven days, source health and a live table of ingested log events.
Log ingestion

01Observability

Telemetry and logs from every source land in one pipeline. Agentic decoders and rulesets parse each event and map it to a detection, so analysts start from context instead of raw lines.

  • Log ingestion
  • Agentic decoders
  • Rulesets
Capabilities

Everything in the platform

5 modules, built from scratch for our partner and run in production by our team.

01

Observability

Telemetry and logs from every source land in one pipeline. Agentic decoders and rulesets parse each event and map it to a detection, so analysts start from context instead of raw lines.

  • Log ingestion
  • Agentic decoders
  • Rulesets
  • Telemetry and log ingestion
  • Agentic decoders and rulesets
02

Asset inventory

A private network scanner discovers every device on internal ranges. AI enriches each asset and rates its confidentiality, integrity and availability risk, with hardware, software and cryptography bills of materials.

  • Hardware BOM
  • Software BOM
  • Crypto BOM
  • CIA risk
  • Hardware, software and cryptography bills of materials (HBOM, SBOM, CBOM)
  • Private network scanner for RFC 1918 ranges (private network ranges)
  • AI-powered asset enrichment
  • AI-powered risk analysis of assets (confidentiality, integrity, availability)
03

Threat detection

An in-house threat intelligence cache aggregates public and vendor feeds. Machine learning flags anomalies across many indicators, and continuous threat exposure management (CTEM) detects active and passive threats with AI remediation for each one.

  • Threat intel cache
  • ML anomaly detection
  • Exposure management
  • In-house global threat intelligence cache (GTIC)6
    • NVD
    • AbuseIPDB
    • MalwareBazaar
    • AlienVault OTX
    • VirusTotal
    • Vendor advisories from Microsoft, Oracle, Red Hat and others
  • Machine learning anomaly detection on logs, covering multiple indicators of compromise
  • Continuous threat exposure management (CTEM)3
    • Real-time detection of active and passive threats
    • AI-powered remediation specific to each threat
    • Remediation management system that tracks unresolved active threats
04

Risk management

Domains are pulled from firewall telemetry and filtered automatically. AI agents assess domains, vendors and systems, run tailored surveys and blacklist high-risk domains before they become incidents.

  • Domain assessment
  • Vendor assessment
  • Blacklisting
  • Domain extraction and filtering from firewall telemetry
  • Agentic domain assessment
  • Agentic vendor assessment
  • Agentic system assessment1
    • System and vendor specific surveys run by agents
  • AI-powered blacklisting of high-risk domains
05

Proactive alerting

Alerts reach the right people as soon as a threat, exposure or risky domain is found, with the context needed to act.

  • Real-time alerts
  • Routing
  • Context
  • Proactive alerting across detection, exposure and risk
Connects to

Sources and feeds

Threat intelligence

  • NVD
  • AbuseIPDB
  • MalwareBazaar
  • AlienVault OTX
  • VirusTotal
  • Vendor advisories
Delivery and operations

How we built and run it

  • Runs in the cloud, on premise or as a hybrid, next to the systems that produce the logs.
  • Logs, asset records and findings stay inside the customer environment. Only public threat feeds come in from outside.
  • Role-based access to every view, with an audit trail of who changed what.
  • Self-hosted models run the AI analysis when telemetry must not leave the network.
  • Built from scratch by SparkAi, which still runs releases, monitoring and new features.